In Safeguard 11.2, we talked about making sure backups happen automatically and frequently enough to meet the needs of the business. Once those copies exist, however, another question immediately follows. How are you protecting them? CIS Safeguard 11.3, Protect Recovery Data, addresses that question. The basic expectation is that recovery data should receive protections equivalent to the original data. If sensitive information requires encryption, restricted access, or other safeguards in...

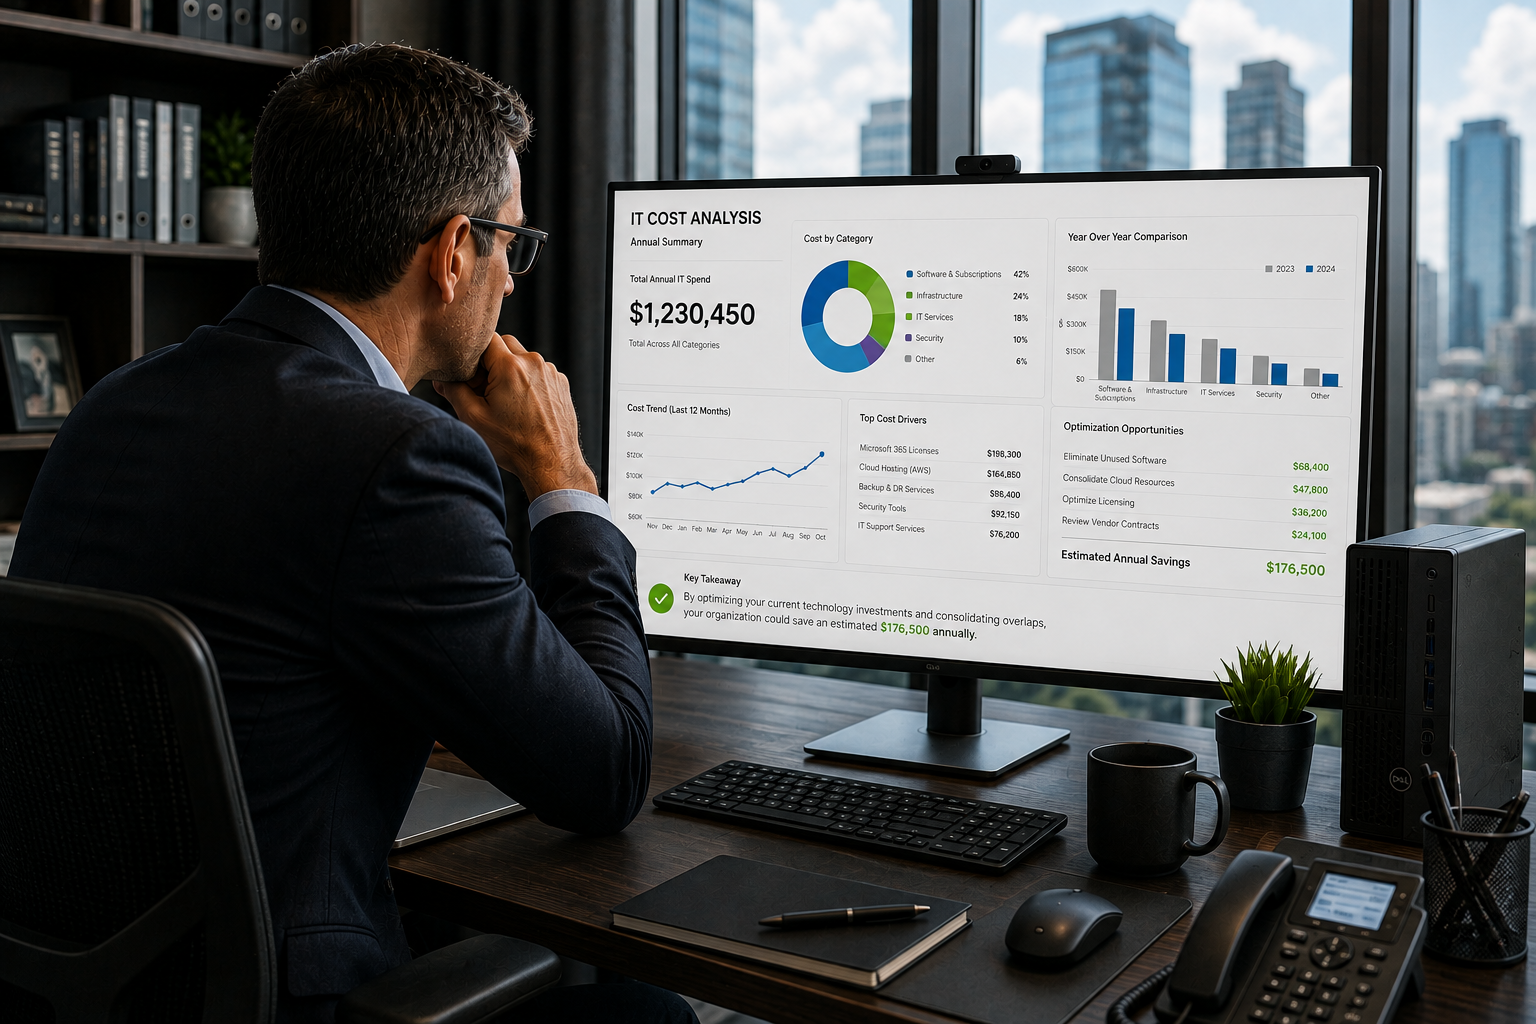

CIS IG1 Control 4.7: Manage Default Accounts on Enterprise Assets and Software
by Heath Gieson Manage Default Accounts on Enterprise Assets and Software As we continue through the CIS IG1 controls, a consistent pattern keeps...
More Updates Don’t Mean More Risk — They Mean Better Security
Why More Updates Are Coming — and Why That’s a Good Thing Over the next several weeks, organizations are likely to notice something familiar but...

CIS IG1 Control 4.6: Securely Managing Network Gear
When the Management Plane Becomes the Attack Plane by Heath Gieson A few years ago, I was sitting in a conference room with an executive team after...
The Unlocked Screen in the Corner Office: What CIS Control 4.3 Requires and Why Biometrics Make It Easier Than You Think
by Heath Gieson Some attacks are sophisticated. Weeks of reconnaissance, carefully crafted phishing emails, vulnerabilities quietly exploited in the...
CIS IG1 Control 3.6: Encrypt Data on End User Devices—Because Lost Doesn’t Have to Mean Exposed
by Heath Gieson As we continue our weekly journey through the CIS IG1 controls, each safeguard builds on the operational foundations we’ve been...

You Cannot Protect What You Have Not Identified
by Tim Marley Last week we talked about data management at a high level. The operating model, the responsibility, the reality that organizations are...
CIS IG1 Control 3.1: Data Management is Not a Policy Problem
by Tim Marley Over the course of my career, and particularly in the last five to ten years, the topic of data management comes up frequently....
CIS IG1 Control 2.3 — Why Unauthorized Software Is a Hidden Threat Lurking on “Trusted” Devices
Most organizations assume that corporate devices only run approved software. In reality, that assumption is often wrong. Users are inherently...

CIS IG1 Control 2.2 — Why Running Supported Software Is a Security Requirement, Not an IT Preference
Most security conversations focus on what software exists in an environment. CIS Control 2.2 pushes the conversation one step further by asking a...
