Disable Autorun and Autoplay for Removable Media One of the oldest tricks in security still works. Leave a few USB drives in a parking lot, a lobby, or a break room, and wait. Someone picks one up, plugs it into a work computer to see what's on it, and if that computer is set to automatically run whatever the drive offers, the attacker just skipped past nearly every other defense you have. Control 10.3 closes that specific door by turning off the feature that lets removable media run on...

Trending at Forthright.
CIS IG1 Control 10.2: Protection Is Only as Current as Its Last Update
CIS IG1 Control 10.1: Table Stakes, but Only If It Can Catch What’s Actually Out There
CIS IG1 Control 9.2: Hanging Up the Call Before It Connects
CIS IG1 Control 9.1: An Unsupported Application Is One the Vendor Has Stopped Defending
CIS IG1 Control 8.3: The Log You Need Is Always the One That Already Rolled Off
Ensure Adequate Audit Log Storage Here's a pattern that repeats in incident after incident. The investigation finally pinpoints the moment that...
CIS IG1 Control 8.2: A Log You Can’t Reach Is a Log You Can’t Trust
Collect Audit Logs There's a predictable early move in a lot of intrusions: once an attacker is on a machine, they clear its local logs. If the only...
CIS IG1 Control 8.1: The Question Every Investigation Starts With
Establish and Maintain an Audit Log Management Process Every security investigation starts with the same question: what actually happened? In a lot...
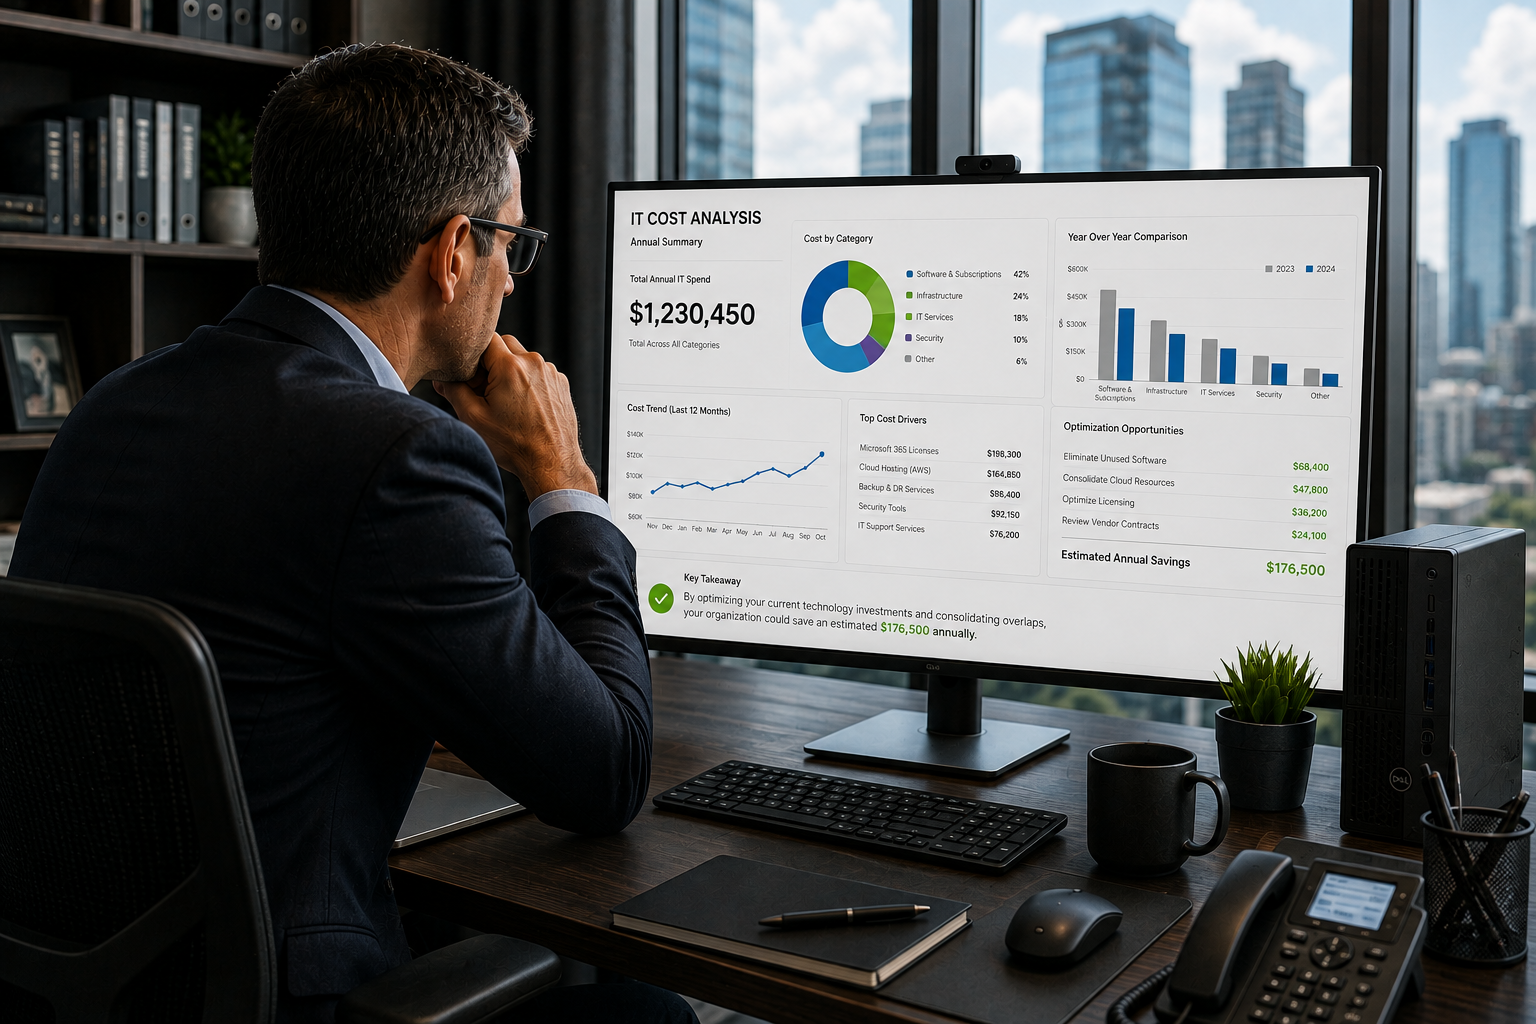
Top Technology Concerns CEOs Are Facing (And Why the Real Risk Isn’t the Technology)
The Top Technology Concerns CEOs Are Facing Today (And Why the Real Risk Isn't the Technology) If you'd asked most CEOs a few years ago what kept...
CIS IG1 Control 7.4: Perform Automated Application Patch Management
Updates You're Probably Not Catching Your operating system is probably the best-patched software on your computers. Modern Windows and macOS update...
CIS IG1 Control 7.3: Perform Automated Operating System Patch Management
Why Patching Should Be a System, Not a Habit Almost no one argues against patching. Every leader I talk to already knows that unpatched systems are...

CIS Safeguard 7.2: Finding the Problem Is Only the Beginning
In Safeguard 7.1, we discussed the difference between running a vulnerability scanner and operating a vulnerability management program. A scan may...

CIS Safeguard 7.1: Why a Vulnerability Scanner Is Not a Vulnerability Management Program
A Vulnerability Scanner Is Not a Vulnerability Management Program As we move into CIS Control 7, Continuous Vulnerability Management, we're going to...
CIS IG1 Safeguard 6.5: Require MFA for Administrative Access
CIS IG1 Safeguard 6.5: Require MFA for Administrative Access by Heath Gieson This final article in the MFA mini‑series focuses on the...
