In Safeguard 11.1, we talked about establishing a data recovery process. Before something fails, the organization needs to understand what has to be recovered, what comes back first, who's responsible, and how recovery is supposed to work. Safeguard 11.2, Perform Automated Backups, takes the next step. CIS requires automated backups of in-scope enterprise assets at least weekly, or more frequently based on the sensitivity of the data. The word "automated" is important. If protecting critical...

Trending at Forthright.
CIS IG1 Control 10.1: Table Stakes, but Only If It Can Catch What’s Actually Out There
CIS IG1 Control 9.2: Hanging Up the Call Before It Connects
CIS IG1 Control 9.1: An Unsupported Application Is One the Vendor Has Stopped Defending
CIS IG1 Control 8.3: The Log You Need Is Always the One That Already Rolled Off

CIS Safeguard 7.2: Finding the Problem Is Only the Beginning
In Safeguard 7.1, we discussed the difference between running a vulnerability scanner and operating a vulnerability management program. A scan may...

CIS Safeguard 7.1: Why a Vulnerability Scanner Is Not a Vulnerability Management Program
A Vulnerability Scanner Is Not a Vulnerability Management Program As we move into CIS Control 7, Continuous Vulnerability Management, we're going to...
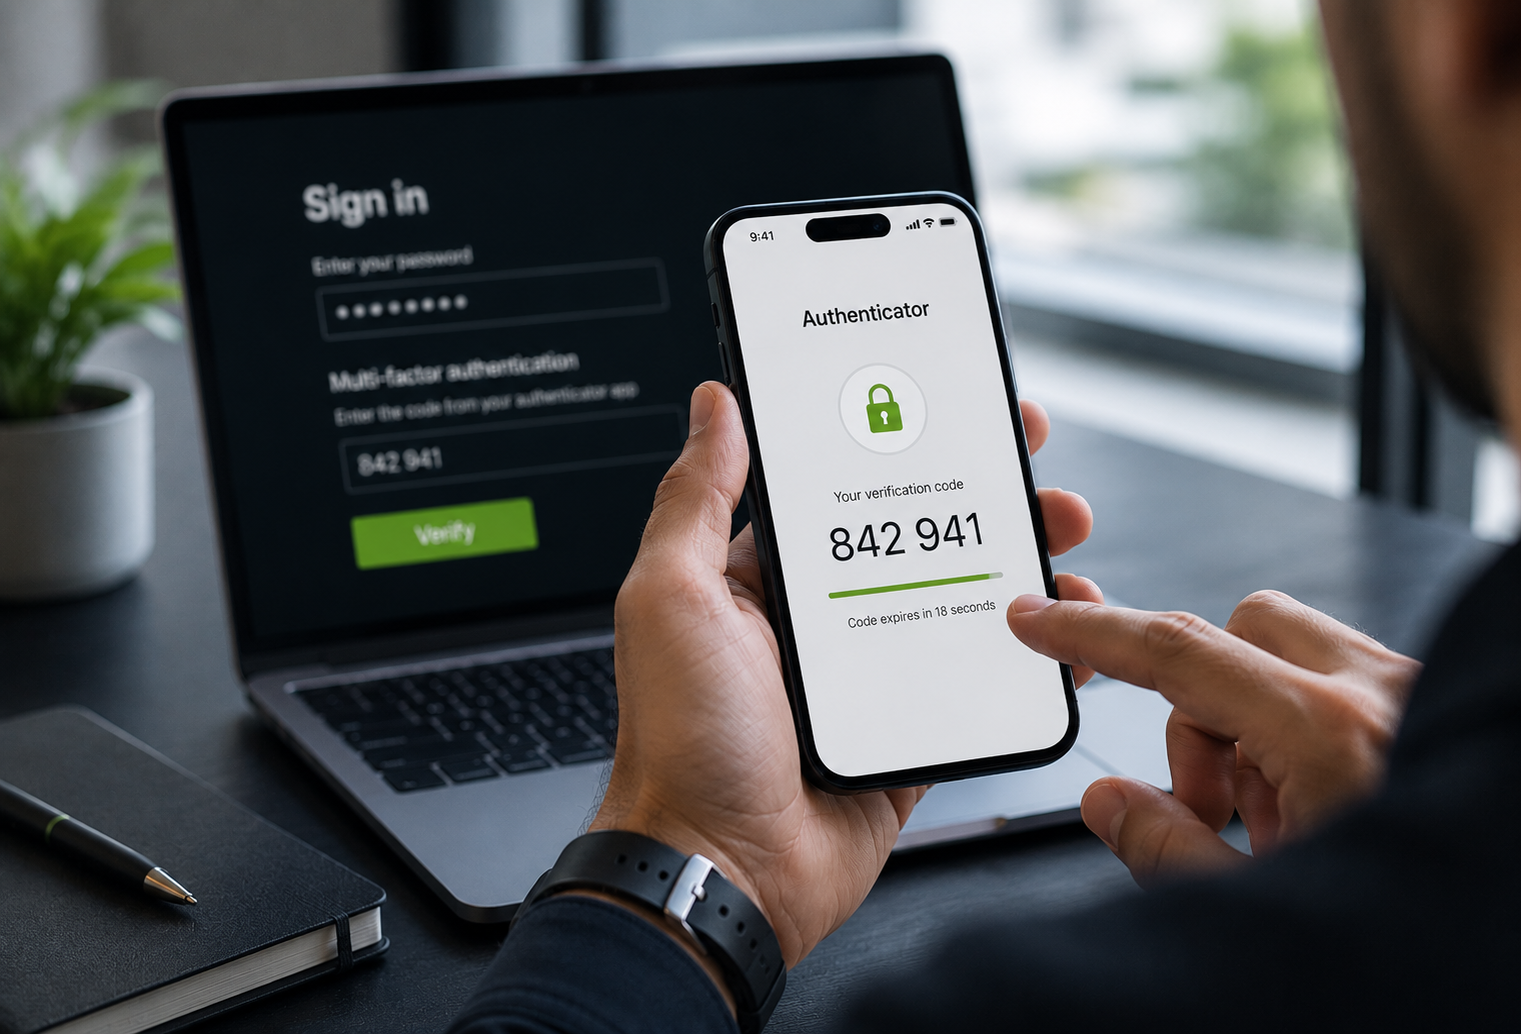
CIS IG1 Safeguard 6.5: Require MFA for Administrative Access
CIS IG1 Safeguard 6.5: Require MFA for Administrative Access by Heath Gieson This final article in the MFA mini‑series focuses on the...
Why 84% of Companies Fail at Digital Transformation. And Why That Number Hasn’t Moved.
Why 84% of Companies Fail at Digital Transformation. And Why That Number Hasn't Moved. By: Frank Merino Nearly a decade ago, Forbes published a...
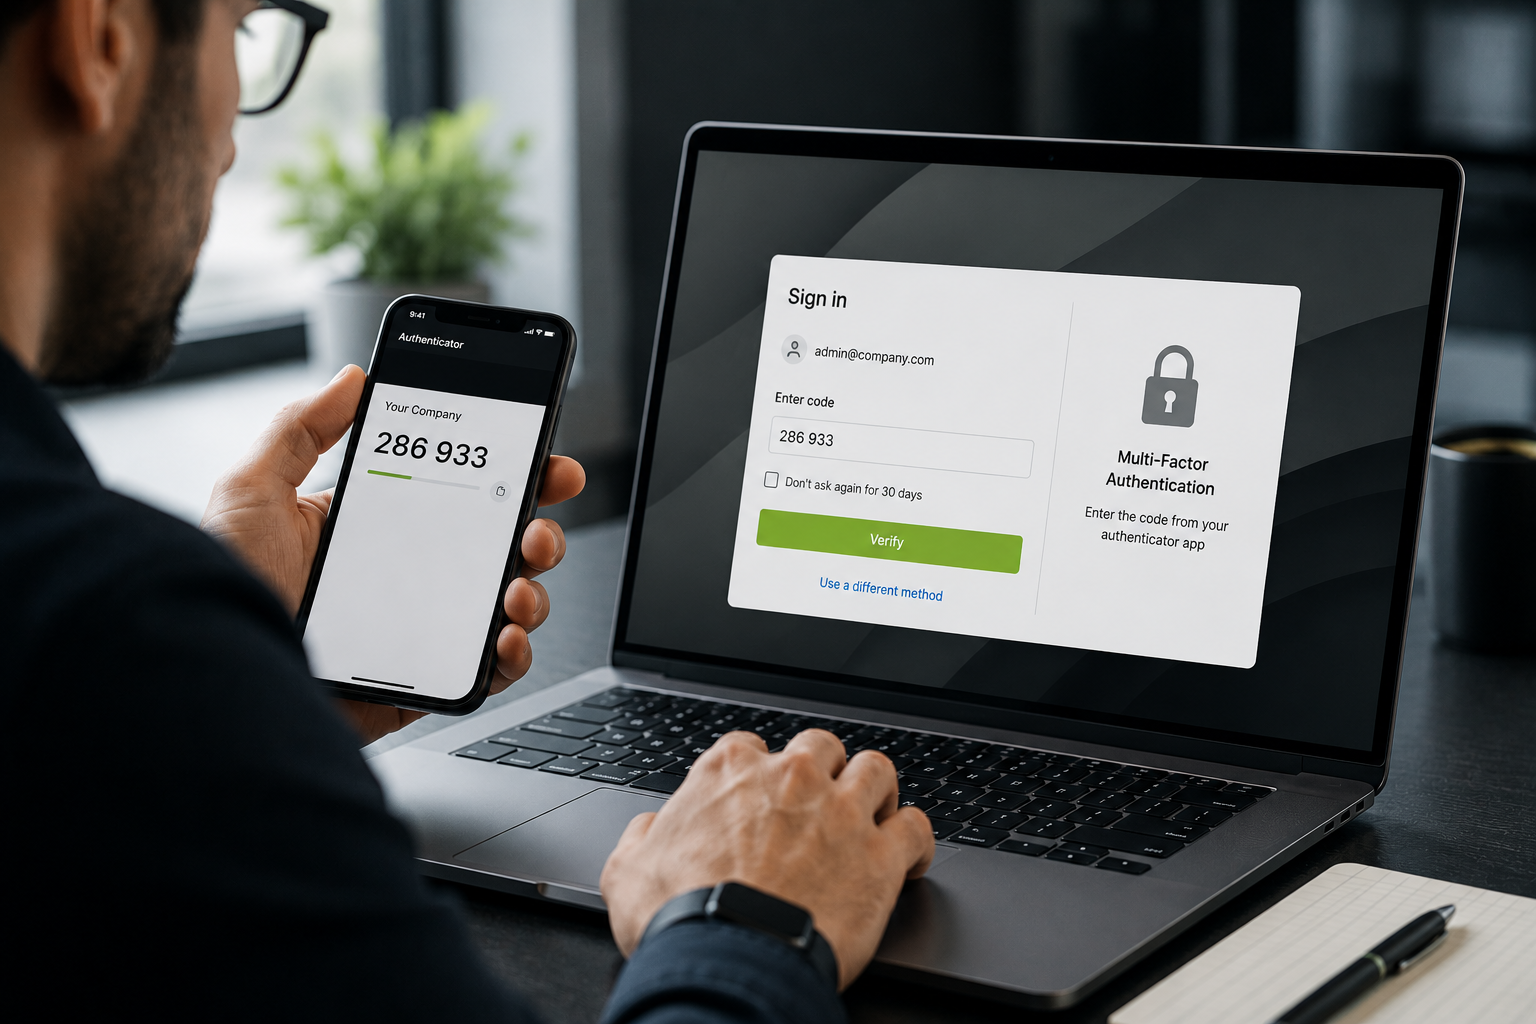
CIS IG1 Safeguard 6.4: Require MFA for Remote Network Access
CIS IG1 Safeguard 6.4: Require MFA for Remote Network Access by Heath Gieson This article continues our CIS IG1 identity series by extending...
CIS IG1 Safeguard 6.3
Require MFA for Externally‑Exposed Applications This article is part of our ongoing CIS IG1 series focused on practical, high‑impact security...
CIS IG1 Control 6.2 – Establish an Access Revoking Process
CIS IG1 Control 6.2 – Establish an Access Revoking Process by Heath Gieson If access granting is where intent is established, access revoking...
Access Control Management: Access Should Be Granted Intentionally
Access Should Be Granted Intentionally By Tim Marley As we move into CIS Control 6, Access Control Management, we're going to spend the next...
CIS IG1 5.4: How Everyday Admin Access Turned a Phish Into a Crisis
by Heath Gieson CIS IG1 Safeguard 5.4 states that administrator privileges should be restricted to dedicated administrator accounts, and that...
