As we move into CIS Control 11, Data Recovery, we're shifting from preventing and detecting problems to something every organization eventually has to face: what happens when something goes wrong. Safeguard 11.1 is Establish and Maintain a Data Recovery Process. CIS expects that process to address the scope of recovery activities, recovery priorities, and the security of backup data. The documentation should also be reviewed at least annually or when significant changes occur. That sounds...

CIS IG1 Control 9.1: An Unsupported Application Is One the Vendor Has Stopped Defending
Ensure Use of Only Fully Supported Browsers and Email Clients Your web browser and your email client are the two applications your people use most,...
CIS IG1 Control 8.3: The Log You Need Is Always the One That Already Rolled Off
Ensure Adequate Audit Log Storage Here's a pattern that repeats in incident after incident. The investigation finally pinpoints the moment that...
CIS IG1 Control 8.2: A Log You Can’t Reach Is a Log You Can’t Trust
Collect Audit Logs There's a predictable early move in a lot of intrusions: once an attacker is on a machine, they clear its local logs. If the only...
CIS IG1 Control 8.1: The Question Every Investigation Starts With
Establish and Maintain an Audit Log Management Process Every security investigation starts with the same question: what actually happened? In a lot...
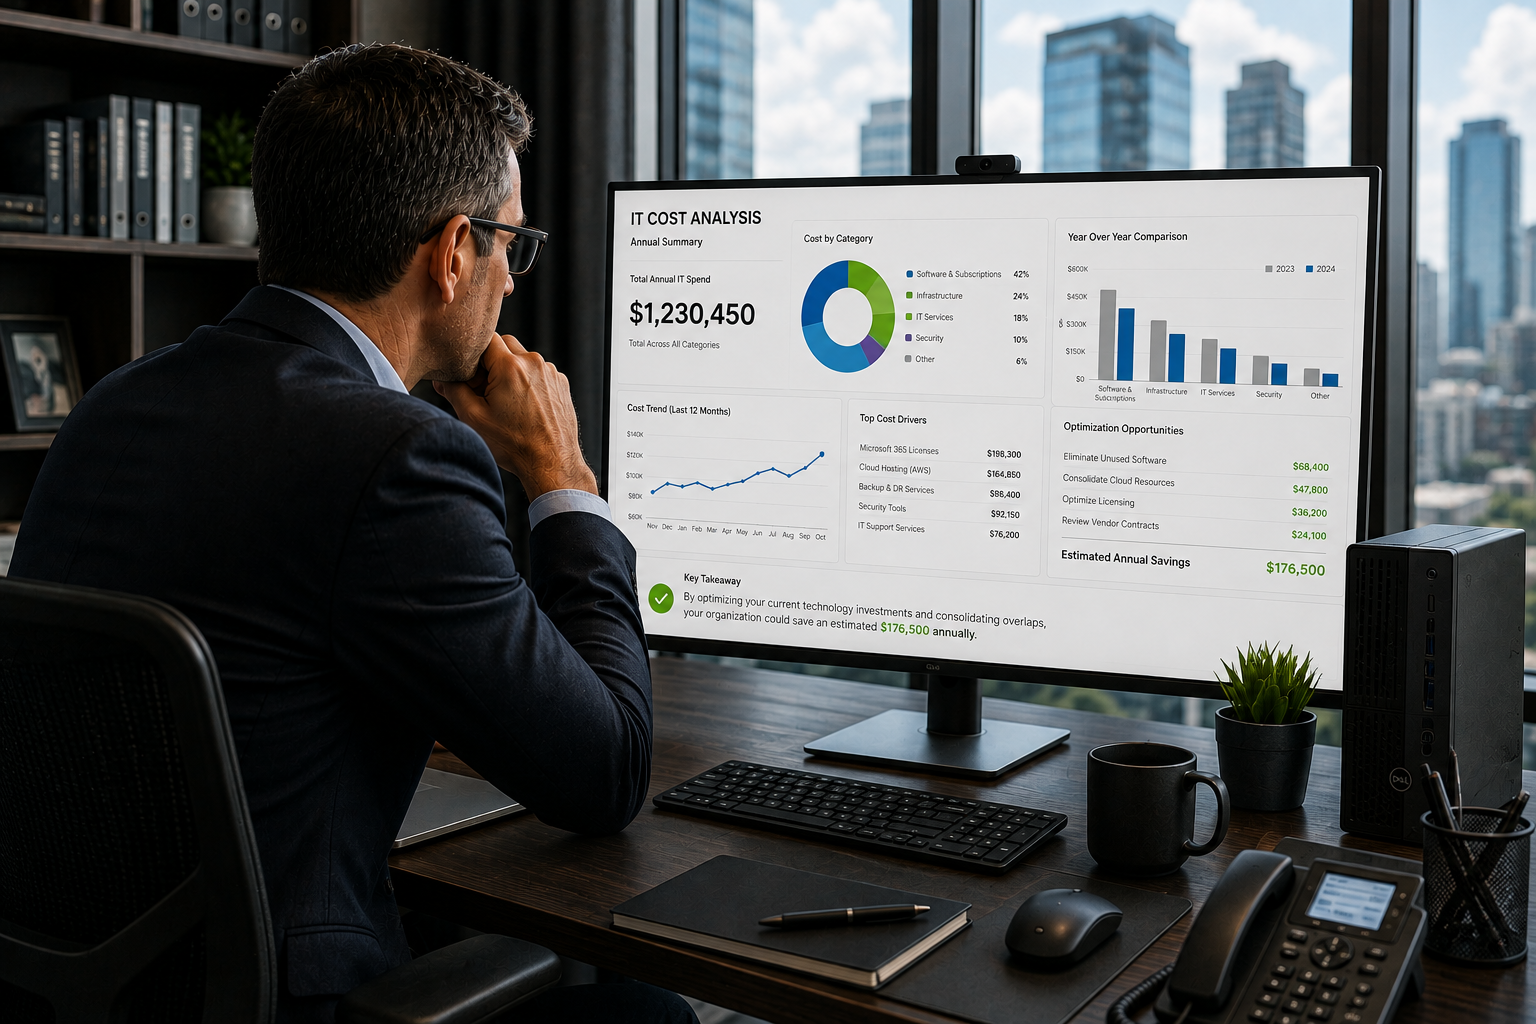
Top Technology Concerns CEOs Are Facing (And Why the Real Risk Isn’t the Technology)
The Top Technology Concerns CEOs Are Facing Today (And Why the Real Risk Isn't the Technology) If you'd asked most CEOs a few years ago what kept...
CIS IG1 Control 7.4: Perform Automated Application Patch Management
Updates You're Probably Not Catching Your operating system is probably the best-patched software on your computers. Modern Windows and macOS update...
CIS IG1 Control 7.3: Perform Automated Operating System Patch Management
Why Patching Should Be a System, Not a Habit Almost no one argues against patching. Every leader I talk to already knows that unpatched systems are...

CIS Safeguard 7.2: Finding the Problem Is Only the Beginning
In Safeguard 7.1, we discussed the difference between running a vulnerability scanner and operating a vulnerability management program. A scan may...

CIS Safeguard 7.1: Why a Vulnerability Scanner Is Not a Vulnerability Management Program
A Vulnerability Scanner Is Not a Vulnerability Management Program As we move into CIS Control 7, Continuous Vulnerability Management, we're going to...
