Healthcare Providers, Experience What Cybersecurity Feels Like.

Without the Commitment.

Put your practice to the test.  Evaluate cybersecurity for your business with up to 90 days of enterprise-level cybersecurity at no cost. Setup is easy, Forthright's team of security experts can get you setup in as little as 30 minutes.   

From Forthright COO Frank Merino:

As an IT Service Provider, we understand the critical importance of maintaining the integrity and availability of our clients’ systems. The recent incident involving CrowdStrike, where a faulty update caused widespread disruptions and led to millions of Windows computers experiencing the “Blue Screen of Death”, serves as a stark reminder of the vulnerabilities that exist in our digital infrastructure.

While this incident specifically involved CrowdStrike, it is essential to recognize that tomorrow it could be your line of business application, Microsoft, or any other critical software. The question we must all ask ourselves is: Are we prepared?

Key Points to Consider:

  1. Incident Response Plan: Do you have a comprehensive incident response plan in place? This plan should outline the steps to take in the event of a system failure or security breach. It is crucial to have a clear and actionable plan to minimize downtime and mitigate the impact on your operations.
  2. Testing the Plan: Having an incident response plan is not enough. Regularly testing and updating the plan is vital to ensure its effectiveness. Conducting simulated incidents and drills can help identify potential weaknesses and improve response times.
  3. Disaster Recovery: Traditionally, disaster recovery has focused on natural disasters such as fires and hurricanes, and more recently, ransomware attacks. However, incidents like the CrowdStrike update highlight that software failures can also be catastrophic. How prepared are you to recover from such an event?
  4. Proactive Measures: Implementing proactive measures such as regular system updates, backups, and monitoring can help prevent incidents and ensure quick recovery. Staying informed about the latest security threats and best practices is essential for maintaining a robust defense.

In conclusion, the CrowdStrike incident is a wake-up call for all organizations. It underscores the need for a well-prepared and tested incident response plan. As your IT Service Provider, we are committed to helping you navigate these challenges and ensure the resilience of your systems. Remember, it’s not a matter of if, but when the next incident will occur. Are you prepared?

Assurance to Our Clients:
We want to assure our clients that Forthright and our ability to deliver our services were not impacted during this outage. Additionally, Forthright has heeded our own advice and reviewed our own solutions and the steps we would take should a similar incident occur. We can all be better because of this and should not stand by idle when we can learn from those who were impacted. We will continue to improve our services and procedures based on our findings.

Healthcare Cybersecurity Services That Protect Patient Data and Keep Care Moving

Healthcare organizations face a difficult balance: protect sensitive patient information, maintain regulatory compliance, support clinical operations, and stay ahead of evolving cyber threats.

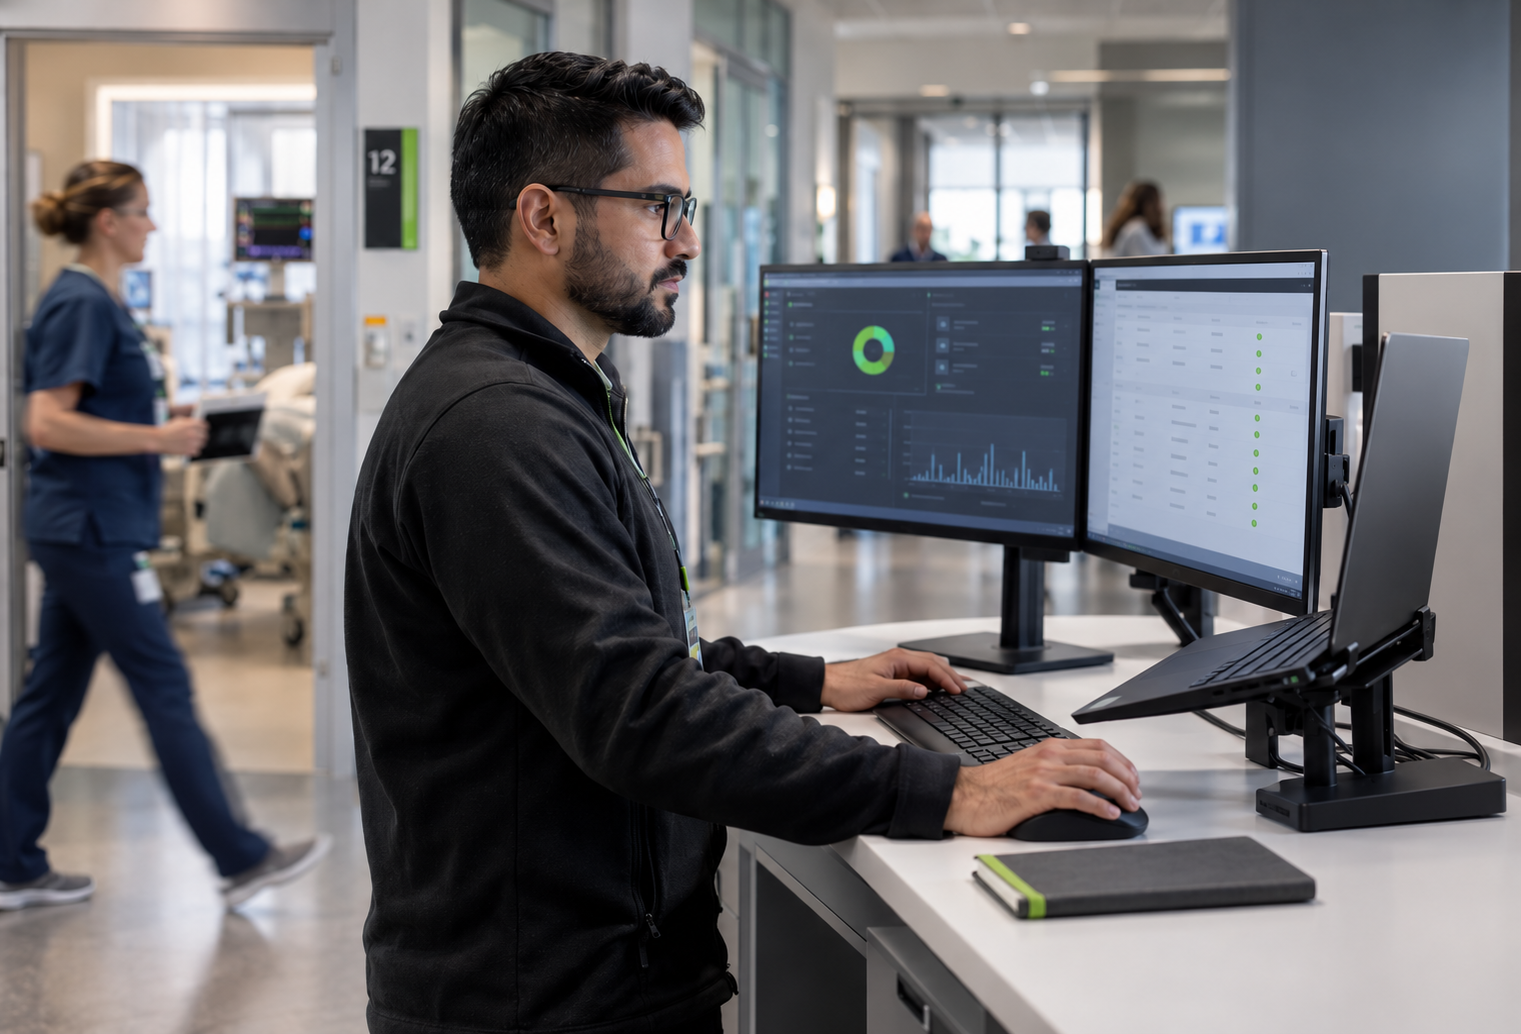
Forthright is a cybersecurity-first IT partner for healthcare organizations, helping providers reduce cyber risk, strengthen HIPAA compliance, protect electronic health records (EHRs), and maintain reliable access to the systems clinicians and staff depend on every day.

How Forthright Protects Healthcare Organizations

HIPAA Compliance and Healthcare Cybersecurity Risk Assessments

Protecting patient data starts with understanding where risk exists.

Our HIPAA compliance and cybersecurity risk assessments help healthcare organizations identify vulnerabilities across IT systems, EHR platforms, networks, endpoints, and patient data environments. We provide clear, actionable guidance to help strengthen your security posture and support ongoing regulatory readiness.

Key areas include:

  • HIPAA security and compliance readiness

  • Healthcare cybersecurity risk assessments

  • EHR and patient data security

  • Vulnerability identification and remediation planning

  • Security policy and control reviews

24/7 Security Operations Center and Real-Time Threat Detection

Cyber threats do not operate on a business-hours schedule.

Forthright provides 24/7 SOC monitoring and managed cybersecurity services designed to identify, analyze, and respond to suspicious activity across your environment. Our security experts help reduce the time between detection and response so your organization can protect sensitive data while minimizing disruption to patient care.

Our always-on protection supports:

  • 24/7 cybersecurity monitoring

  • Real-time threat detection and response

  • Managed security operations

  • Network and endpoint visibility

  • Incident identification and escalation

Healthcare Security Awareness Training for Employees

Technology alone cannot protect patient information.

Healthcare employees regularly interact with email, patient records, cloud applications, mobile devices, and other systems that can become entry points for cyber threats. Our healthcare cybersecurity awareness training helps employees recognize phishing attacks, practice secure data handling, protect devices, and follow security best practices.

Training helps strengthen your human layer of defense while supporting a more security-aware healthcare organization.

Multi-Factor Authentication and Secure Access Controls

Strong identity and access management helps ensure that the right people have access to the right systems.

Forthright helps healthcare organizations implement multi-factor authentication (MFA), secure access controls, and password management practices to reduce unauthorized access to EHR systems, patient portals, cloud applications, and other sensitive resources.

Learn more about identity and access management and MFA.

Managed Cybersecurity for Healthcare Organizations

Whether you operate a small medical practice, specialty clinic, multi-location healthcare organization, or larger provider network, Forthright helps you build a more secure and resilient technology environment.

Our cybersecurity-first approach helps healthcare organizations:

  • Reduce cyber risk

  • Protect patient data

  • Strengthen HIPAA compliance readiness

  • Improve security monitoring and response

  • Reduce operational disruption

  • Maintain patient trust

  • Keep clinicians and staff productive

Forthright brings cybersecurity, IT operations, and executive guidance together so your team can stay focused on what matters most: delivering reliable patient care.

Strengthen Your Healthcare Cybersecurity Strategy

Protecting healthcare systems requires more than security tools. It requires continuous monitoring, strong processes, informed employees, and experienced guidance working together.

Contact Forthright today to learn how our healthcare cybersecurity services, HIPAA compliance support, 24/7 SOC monitoring, and managed IT solutions can help protect your organization and support secure, uninterrupted care.

CHOOSE FORTHRIGHT

One partner for cybersecurity, compliance, and transformation.

We align security, compliance, and technology to reduce risk, keep operations running, and support your growth.

Protect Your Business From Cyber Threats

You’re concerned about ransomware, data breaches, or gaps in your current environment.

Get Expert Guidance on IT, Risk, and Compliance

You’re making decisions around cybersecurity, insurance, or long-term planning.

Modernize and Streamline Operations

Improve productivity with AI, automation, and smarter workflows that reduce friction across your business.

SPECTRA-CERTIFIED CYBERSECURITY WITH CYBER WARRANTY PROTECTION

Forthright is SPECTRA certified, meaning our cybersecurity approach is independently validated against proven security standards.

For your business, that means:

  • Cyber warranty protection for covered incidents
  • Alignment with cyber insurance requirements
  • Potential for improved insurance eligibility and preferred policy rates