• Solutions
    • Forthright DigitalNOW
    • Forthright Advisory
    • Forthright Cyber
  • Tech Insights
  • Events
  • About
  • Contact Us
  • Client Hub

CIS IG1 Control 8.2: A Log You Can’t Reach Is a Log You Can’t Trust

by Heath Gieson | Sep 16, 2026

Collect Audit Logs There’s a predictable early move in a lot of intrusions: once an attacker is on a machine, they clear its local logs. If the only record of what happened lives on the same computer that was compromised, you’ve effectively handed the person you’re investigating the ability to edit the evidence. Control 8.2 solves that by getting your logs off the individual machines and into a place an attacker can’t quietly reach. If 8.1 was the decision about what to...

Trending at Forthright.
CIS IG1 Control 8.1: The Question Every Investigation Starts With

Top Technology Concerns CEOs Are Facing (And Why the Real Risk Isn’t the Technology)

Top Technology Concerns CEOs Are Facing (And Why the Real Risk Isn’t the Technology)

CIS IG1 Control 7.4: Perform Automated Application Patch Management

CIS IG1 Control 7.4: Perform Automated Application Patch Management

CIS IG1 Control 7.3: Perform Automated Operating System Patch Management

CIS IG1 Control 7.3: Perform Automated Operating System Patch Management

CIS Safeguard 7.2: Finding the Problem Is Only the Beginning

CIS Safeguard 7.2: Finding the Problem Is Only the Beginning

by Tim Marley | Jul 22, 2026 | Secure IT operations, Tech Insights

In Safeguard 7.1, we discussed the difference between running a vulnerability scanner and operating a vulnerability management program. A scan may...

read more...
Vulnerability Scanner

CIS Safeguard 7.1: Why a Vulnerability Scanner Is Not a Vulnerability Management Program

by Tim Marley | Jul 15, 2026 | Secure IT operations, Tech Insights

A Vulnerability Scanner Is Not a Vulnerability Management Program As we move into CIS Control 7, Continuous Vulnerability Management, we're going to...
read more...
CIS IG1 Safeguard 6.5: Require MFA for Administrative Access

CIS IG1 Safeguard 6.5: Require MFA for Administrative Access

by Heath Gieson | Jul 8, 2026 | Modern IT Operations, Tech Insights

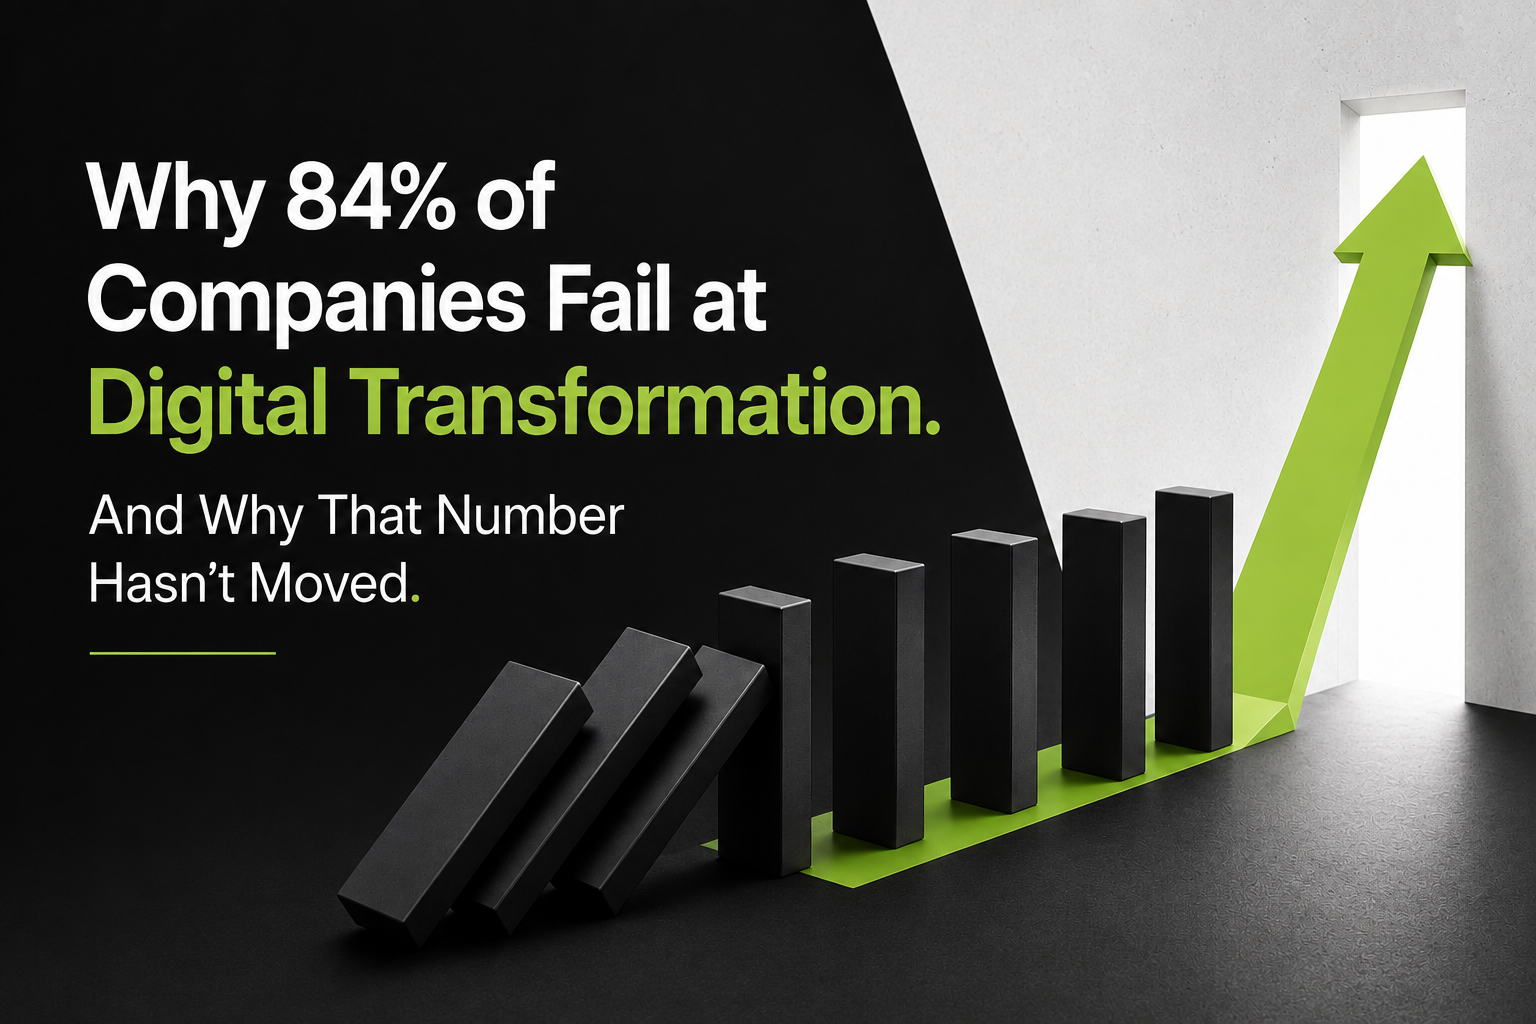
CIS IG1 Safeguard 6.5: Require MFA for Administrative Access by Heath Gieson   This final article in the MFA mini‑series focuses on the...
read more...
Why 84% of Companies Fail at Digital Transformation. And Why That Number Hasn’t Moved.

Why 84% of Companies Fail at Digital Transformation. And Why That Number Hasn’t Moved.

by Frank Merino | Jul 7, 2026 | Modern IT Operations, Tech Insights

Why 84% of Companies Fail at Digital Transformation. And Why That Number Hasn't Moved. By: Frank Merino Nearly a decade ago, Forbes published a...
read more...
CIS IG1 Safeguard 6.4: Require MFA for Remote Network Access

CIS IG1 Safeguard 6.4: Require MFA for Remote Network Access

by Heath Gieson | Jul 1, 2026 | Modern IT Operations, Tech Insights

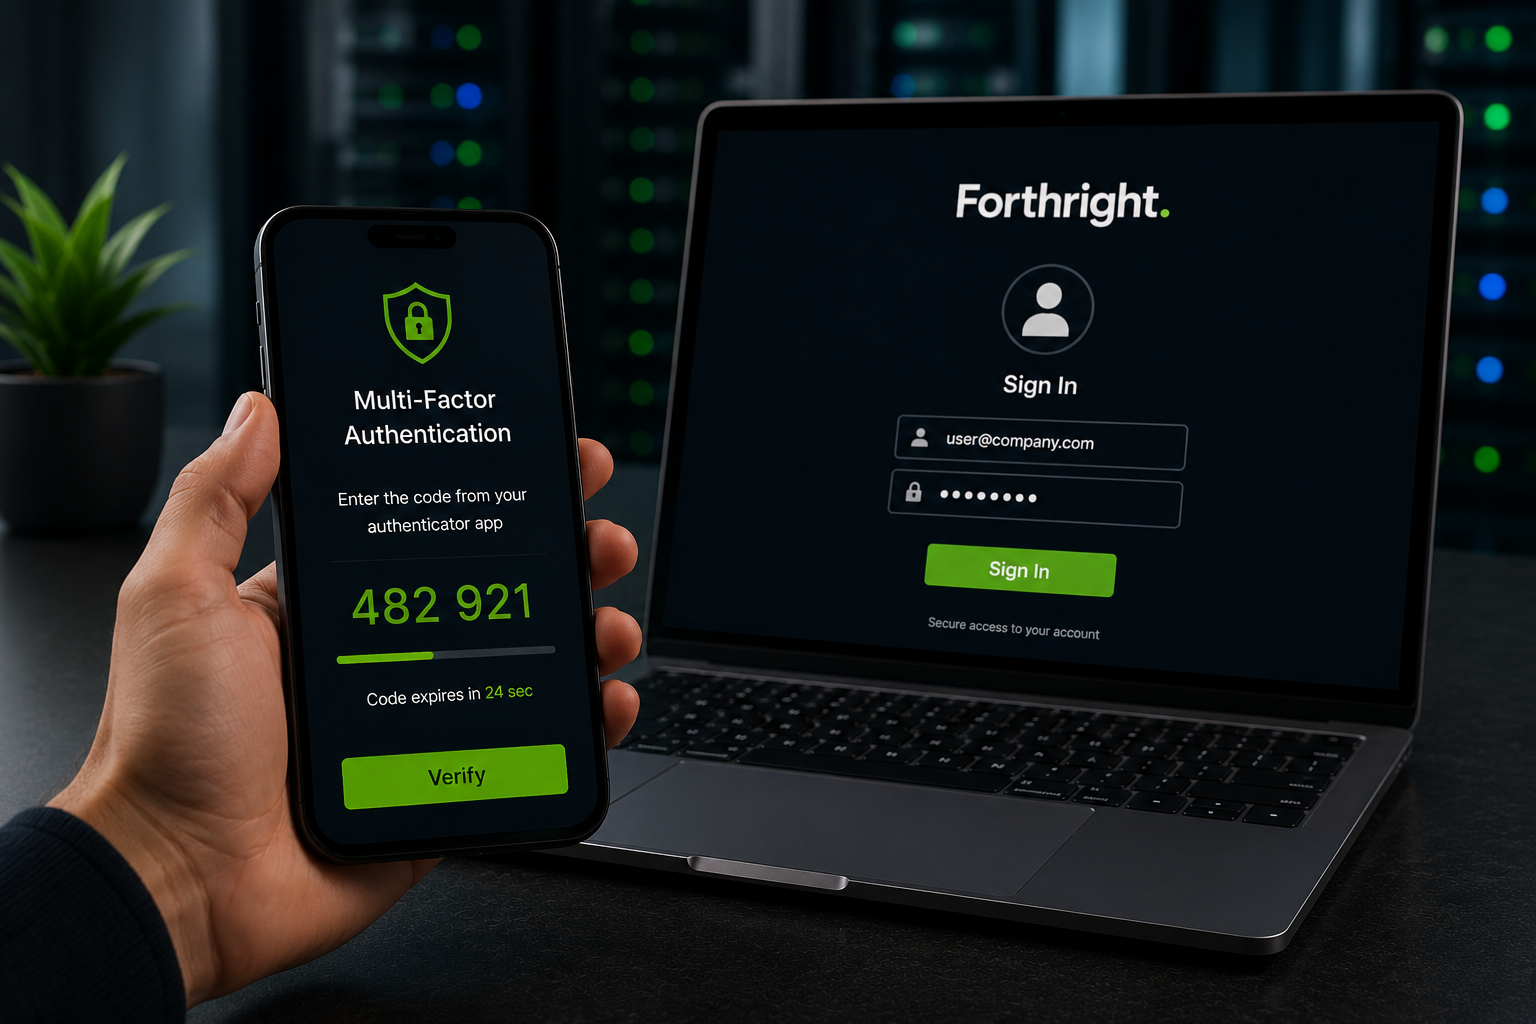
CIS IG1 Safeguard 6.4: Require MFA for Remote Network Access by Heath Gieson   This article continues our CIS IG1 identity series by extending...
read more...
Require MFA for Externally‑Exposed Applications

CIS IG1 Safeguard 6.3

by Heath Gieson | Jun 30, 2026 | Modern IT Operations, Tech Insights, Uncategorized

Require MFA for Externally‑Exposed Applications This article is part of our ongoing CIS IG1 series focused on practical, high‑impact security...
read more...
Access Revoking Laptop

CIS IG1 Control 6.2 – Establish an Access Revoking Process

by Heath Gieson | Jun 30, 2026 | Modern IT Operations, Tech Insights, Uncategorized

CIS IG1 Control 6.2 – Establish an Access Revoking Process by Heath Gieson   If access granting is where intent is established, access revoking...

read more...
Access Control Management: Access Should Be Granted Intentionally

Access Control Management: Access Should Be Granted Intentionally

by Tim Marley | Jun 10, 2026 | 2026, Secure IT operations, Tech Insights

Access Should Be Granted Intentionally   By Tim Marley As we move into CIS Control 6, Access Control Management, we're going to spend the next...
read more...
CIS IG1 5.4: How Everyday Admin Access Turned a Phish Into a Crisis

CIS IG1 5.4: How Everyday Admin Access Turned a Phish Into a Crisis

by Heath Gieson | Jun 3, 2026 | 2026, Secure IT operations, Tech Insights

by Heath Gieson   CIS IG1 Safeguard 5.4 states that administrator privileges should be restricted to dedicated administrator accounts, and that...

read more...
Page 1 of 3012345...102030...»Last »

Every organization has technology goals.

Your business has unique goals, challenges, and opportunities. Our advisory team specializes in helping organizations built on Microsoft technologies. We take the time to understand where you are today, where you want to go, and the obstacles standing in the way. From there, we provide the strategic guidance needed to align technology, cybersecurity, and business priorities.

Gain clarity. Build momentum.
Scale with confidence.

Understand Your IT Priorities | Align Technology and Strategy | Strengthen Operations | Support Growth

Schedule a Call

Let's discuss your business and technology goals.

  • Follow
  • Follow
  • Follow
  • Follow
  • Follow
  • Follow
  • Follow

Explore

Contact Us
About Us
Careers
Events
Blog
Refer a client

Offices

HEADQUARTERS

2893 Executive Park Drive, Suite 204. Weston, FL 33331

(855) 796-3381

Forthright Technology Partners
Certified Minority-owned Business

© 2026 Forthright Technology Partners, Inc.

Sitemap
Privacy Policy
Client Portal
Website Accessibility Statement

Ticket submitted!

Please warm transfer call to (754) 356-1601.